Cloud security & DevSecOps

Your partner
in security.

Your engineers should be building product—not chasing scanner alerts or pulling screenshots for an audit. Gritt works alongside them to fix cloud risk and make secure delivery part of the everyday workflow.

AWSGCPAzureKubernetesSOC 2PCI DSS
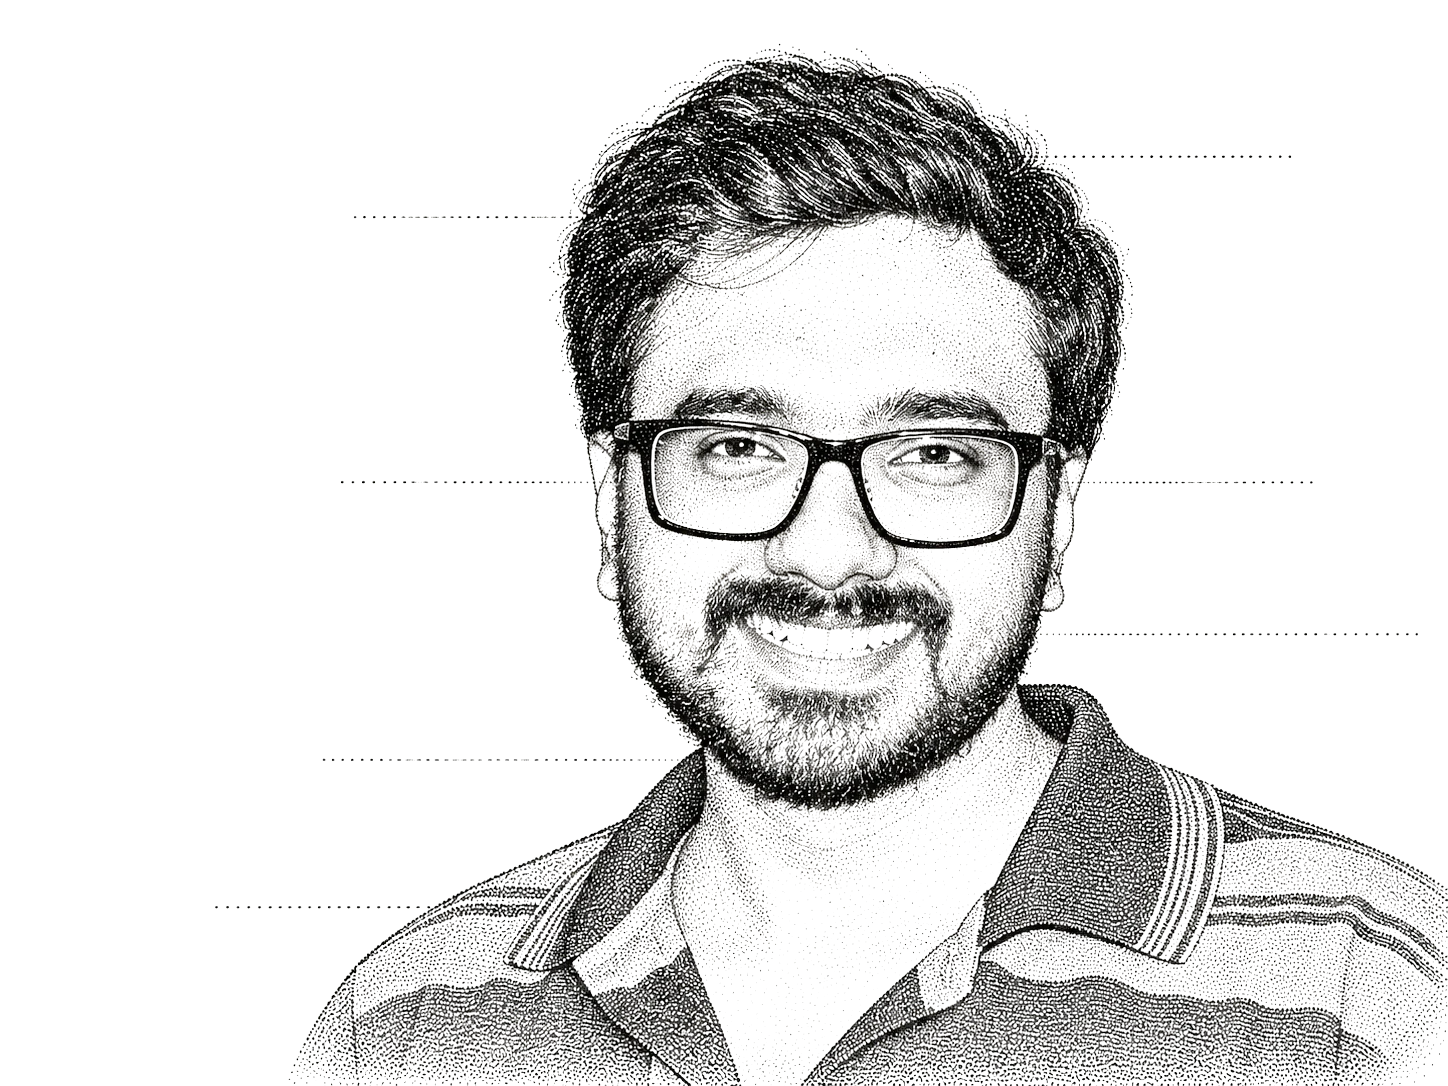
Abhijit from the Gritt engineering team
Engineer on duty ✓ 12+ years of experience

A few teams we’ve worked with

Gritt Lens

Cloud, security and compliance engineers by the hour.

Scheduled sessions are $150. Priority engineering is $250 per hour, with an engineer assigned within one hour.

View Gritt Lens →

01 / The problem

Security gets complicated before most companies are ready to hire a whole team for it.

The backlog starts quietly: an over-permissioned AWS role, a vulnerability report nobody owns, evidence due for an audit next month. We take that work off the pile and fix it with your engineers—not around them.

02 / What we do

The work that keeps getting pushed to next sprint.

We don’t stop at a report. We make the changes, document what matters, and stay close enough to keep things working when the architecture changes.

01

Put the checks where code ships

We add useful security gates to CI/CD, tune out the noise, and make sure someone owns what fails.

DevSecOps services →
  • SAST, DAST & SCA
  • Secrets management
  • Infrastructure as code
  • Container security
02

Tighten up the cloud

We review identities, networks, clusters, logs, and secrets—then work through the risky parts in a sensible order.

Cloud security assessments →
  • Cloud security architecture
  • Identity & access
  • Monitoring & response
  • Threat modelling
03

Get through the audit without the scramble

We map the controls, automate the evidence we can, and help your team answer the questions that still need a human.

SOC 2 readiness →
  • SOC 2 readiness
  • PCI DSS & HIPAA
  • Policy as code
  • Automated evidence
04

Ship AI without exposing the wrong data

We look at how data reaches the model, who can access it, what gets logged, and where an AI feature can be abused.

See all services →
  • LLM application security
  • Model deployment
  • Data protection
  • AI governance

04 / How it works

Start with the mess.
Leave it better.

Every engagement is different, but the working style is simple: get close to the system, fix the important things first, and explain the trade-offs as we go.

  1. 01

    Look under the hood

    We talk to the people who built the system, review the setup, and agree on what needs attention now versus later.

    1–2 weeks
  2. 02

    Work through the list

    We make changes in the repo and the cloud alongside your team. You can see the work, review it, and understand why it is there.

    4–12 weeks
  3. 03

    Stay close after launch

    Security drifts as systems change. We keep an eye on it, tune the noisy parts, and help when something new lands.

    Ongoing

A useful test

Good security should feel boring on a normal Tuesday.
It runs on its ownIt tells you when it breaksThe team knows who owns it

05 / Let’s work

What are you trying to fix?

Maybe an audit is coming up. Maybe the cloud setup has outgrown its early decisions. Send us the context—you’ll hear back from an engineer, not a sales queue.

A short note is fine. We’ll ask the useful questions on the call.